
In this article
In this article
Attackers rarely begin with perfect knowledge of an environment. They explore. They look for services. They test what responds. They follow names, configurations, credentials, applications, databases and infrastructure that appear useful.
That exploration creates an opportunity for defenders. But only if there is something convincing enough to explore. An obvious trap may generate a connection. A believable environment can reveal intent.
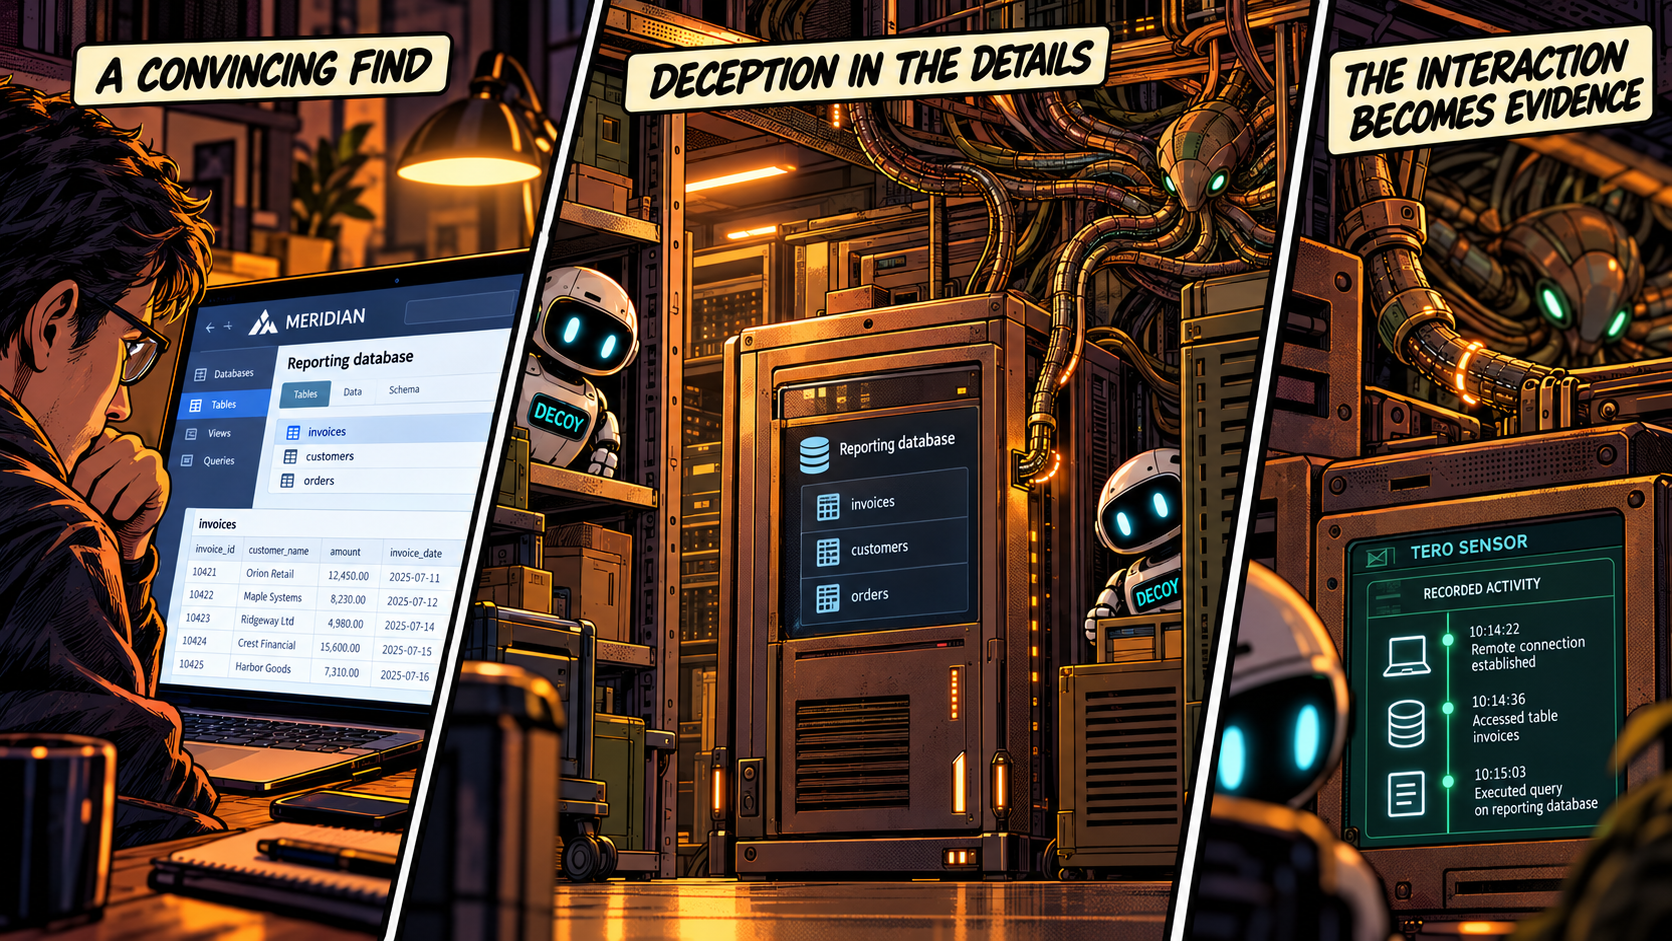
Attackers follow clues
Reconnaissance is often a process of forming a picture. A service is discovered. That service reveals another system. A hostname suggests a database. An application configuration references an internal API. A deployment points toward a container registry. Each discovery answers one question and creates another. The attacker keeps moving because the environment continues to make sense.
That is why the quality of a decoy should not be judged only by whether a port is open. The more important question is: Does the system give someone a believable reason to continue investigating?
Obvious traps end the conversation
Imagine discovering a server called:
honeypot-dbwith:
admin / password123and five obviously fake records. There is very little mystery. Even if it generates an event, the interaction may end immediately.
Now compare that with:
mongo-01.internalcontaining realistic application data, sensible collection names and references to other infrastructure that appears to belong to the same organization. That creates questions: What application uses this? Where is the API? Is there another database? What is running this workload? Where are its containers stored? Every additional question creates another opportunity to observe behavior.
Believability is about coherence
A convincing decoy does not need to contain real information. In fact, it should not. What matters is that the synthetic environment is internally consistent. For example:
Kubernetes
    ↓
references payments-api

Container Registry
    ↓
contains payments-api

Application config
    ↓
references MongoDB and Redis

MongoDB
    ↓
contains related application records

Object Storage
    ↓
contains matching exports
Nothing has to be real. But everything should agree. That coherence helps an environment withstand more than a superficial glance.
We cover the implementation principles behind this in How to Implement Decoys That Attackers Actually Believe.
Curiosity creates evidence
The useful part of attacker exploration is not simply that somebody connected. It is what they choose to do next. Consider the difference between:
connection opened
connection closed
and:
connection
→ service discovery
→ database enumeration
→ collection discovery
→ query activity
→ exploration of another service
The second sequence tells a much richer story. The attacker is making decisions. Those decisions help defenders understand what they were interested in and how they were navigating the environment. The decoy has moved from being a tripwire to becoming an observation point.
Realism can increase the quality of the signal
More interaction does not automatically mean better security. But meaningful interaction can provide stronger context. An attacker who attempts to enumerate a service is showing more interest than someone whose scanner touched a port once. Someone who follows a clue from one decoy to another is revealing even more. That is where believable infrastructure becomes particularly useful. It creates opportunities to distinguish incidental contact from deliberate exploration.
This idea connects directly with Why High-Confidence Detection Matters More Than More Alerts.
The goal is not to fool someone forever
A decoy does not need to survive unlimited scrutiny. That is not the objective. The objective is to remain convincing long enough for unauthorized exploration to become visible and useful.
If someone spends time investigating a synthetic database instead of immediately dismissing it, the decoy has already created value. If they follow references into another synthetic service, the defender learns even more. The advantage comes from turning attacker curiosity into evidence.
Give exploration somewhere to go
Attackers need information to make their next decision. If every believable path leads only toward real infrastructure, defenders have fewer opportunities to observe that decision-making safely. Realistic decoys change that. They give exploration somewhere else to go. Somewhere controlled. Somewhere observable. Somewhere interaction has meaning. That is why a strong decoy should not simply say:
“You found me.
It should make the attacker think:
“This might be useful.
And give the defender time to see what happens next.
To see how Tero turns those interactions into evidence:
What Happens When an Attacker Touches a Tero Decoy? →
Or see the experience directly: