
01 / Discovery
An engineering service draws interest.
Someone discovers a repository, artifact service or project share represented by a Tero Decoy in an approved support segment.
Tero deploys realistic Decoys around engineering repositories, shared files and internal support services. Reveal suspicious exploration and capture the evidence your security team needs to investigate.
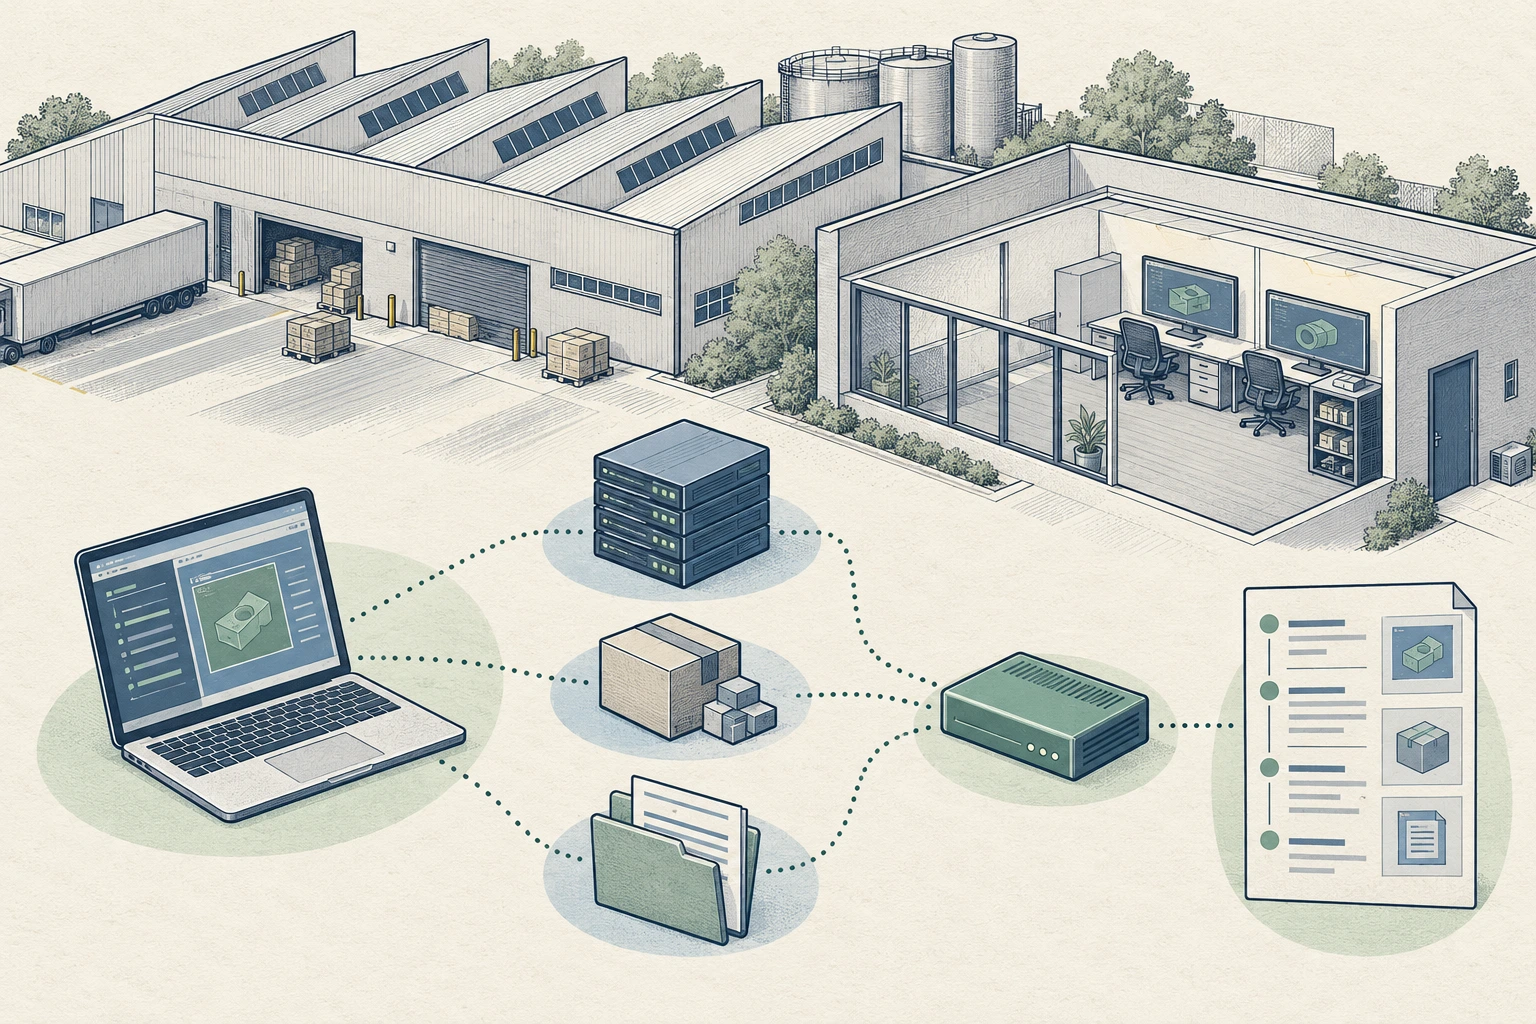
Reveal support-service exploration.Watch interactions with realistic Decoys.
Keep the engineering context.Link the activity to its deployment.
Investigate the recorded sequence.Review the requests and observed outcomes.
A repository, artifact service or shared workspace can look like a useful foothold. A Decoy gives the interaction a believable setting and your team evidence to investigate.
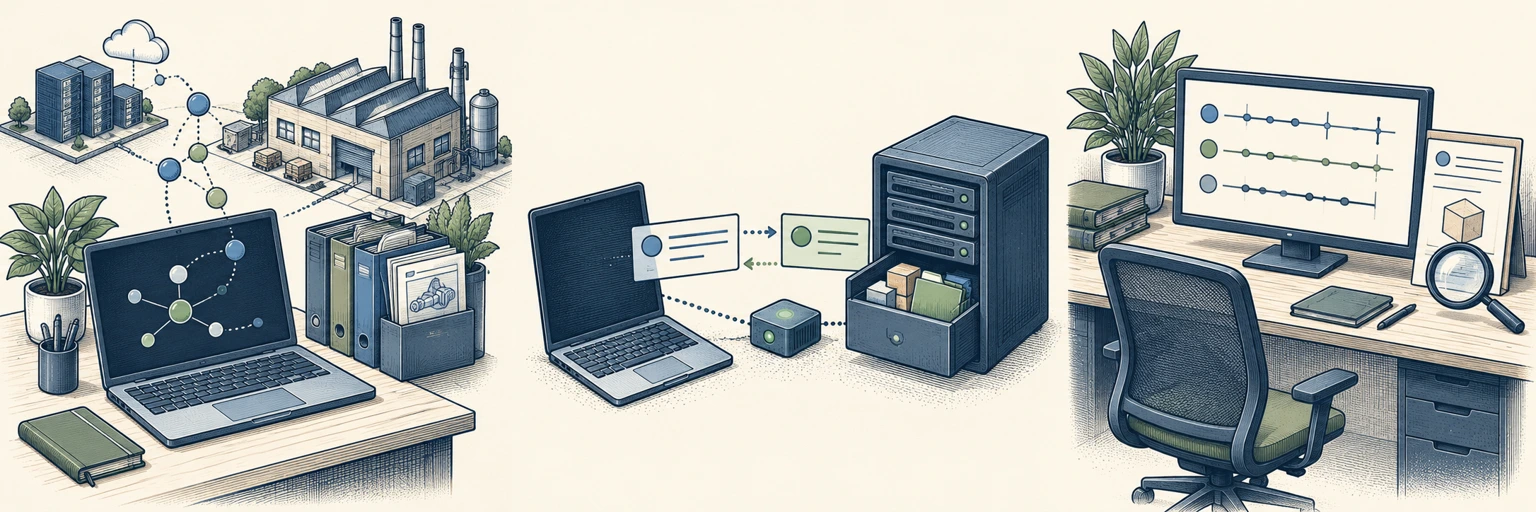
Someone discovers a repository, artifact service or project share represented by a Tero Decoy in an approved support segment.
Synthetic project content gives the service a credible purpose. Supported interactions capture requests and observed responses.
Review the observed source, target and session alongside the engineering or business environment involved.
Choose relevant Decoys for approved business and engineering support networks. Start with the services an intruder may explore.
Represent code repositories, CI/CD consoles and artifact services using synthetic projects and packages. Follow discovery, retrieval and supported action attempts.
Make selected project shares, finance folders and supplier exchanges look relevant. Record browsing and access attempts against synthetic business content.
Represent supported reporting databases, access services and support portals. Keep suspicious interactions tied to the right segment and deployment context.
Capability availability depends on the verified Sensor release and host requirements. Use synthetic projects, packages and documents in approved support networks.
Tero brings the recorded requests and outcomes into one investigation. Your team can follow discovery and retrieval activity through to a restricted publication attempt.
Recorded activity against a Decoy with synthetic build artifacts.
Synthetic project package listingSynthetic engineering packageRepository write operationHuman identity, production changes and operational impact remain unconfirmed.
Place a Sensor on an approved, supported host in your business or engineering-support environment. Plan the network scope with the infrastructure owners and configure private access to the Decoys.
Select approved IT support segments with the relevant IT and operations owners.
Choose supported Decoys and synthetic project, package or document content.
Confirm readiness, source attribution, recorded outcomes and investigation context.
This example represents support IT services. It does not depict monitoring of industrial controllers, production machinery or control-system traffic.
Use an approved business or engineering-support host and segment. Agree the scope, access paths and boundaries with the relevant infrastructure and operations owners before installation.
This solution describes supported Decoys for business and engineering IT services. It does not claim industrial-control-protocol coverage, monitoring of machinery or protection of production control systems.
No. Use synthetic projects, documents and artifacts. Do not copy proprietary designs, real build packages, operational configurations or production credentials into Decoys.
Decoy readiness, separate-client access, observed-source attribution, recorded requests and responses, correct engineering context and the investigation workflow for each selected capability.
Tell us about the repositories, shared services and support networks you want to monitor. We’ll help you plan a focused detection layer for your environment.
Plan your deploymentStart with a defined scope. Verify the evidence.