In this article
In this article
Your Business Is Growing. Is Your Security Keeping Up?
As your business expands, keep track of the systems and access paths that matter.
The first version of your business was easier to understand. A small team, a handful of applications and someone who knew how everything connected.
Then you hired more people. Added a customer platform. Moved an application into the cloud. Gave a supplier access to an internal service. Kept an older system running because the business still depended on it.
Each decision made sense. Together, they created an environment that takes more effort to oversee.
For a growing company, the question becomes practical: if something suspicious happened inside that environment, would your team know where to look?
Growth creates more places to watch
Your security responsibilities expand alongside your operations. Finance needs access to business records. Customer teams depend on internal applications. Developers work with databases and deployment services. Remote employees need reliable ways to connect.
Those systems support the company. They also create access paths your team needs to understand and manage.
The challenge is often ownership. One person may manage infrastructure, another handles applications, and an external provider looks after part of the network. Nobody should have to reconstruct those relationships from memory during an investigation.
Start by identifying the resources that keep your business working. Then ask who should reach them, which systems depend on them and what would make an interaction unexpected.
More information needs to lead to clearer decisions
Logs and alerts are useful when they help someone decide what to do next. A connection notification with little context can leave a busy team with several unanswered questions.
Was the source an administrator? Did access succeed? Was anything read? Did the client attempt another action? Could the activity belong to an authorized test?
Good detection gives your team something specific to investigate and enough evidence to begin.
That is particularly valuable when the people responsible for security also manage support, infrastructure and the next business project.
A useful signal gives your team a starting point and evidence to examine.
Introduce a resource with a clear detection purpose
A Decoy is a realistic service or resource created for detection, using synthetic content rather than production business data. It could resemble a reporting database, an internal portal or another service that fits its surroundings.
Because ordinary business workflows do not depend on it, an unexpected interaction gives your team a focused reason to look closer.
Consider a synthetic reporting database placed in a network used by application workloads. An unfamiliar client connects, lists tables and attempts to read records. The useful outcome is a record of that interaction: what was attempted, what succeeded and what the service returned.
Your team still needs to distinguish suspicious behaviour from expected activity such as scanning, administration and testing. The Decoy provides a deliberate observation point and evidence to support that assessment.
Choose one business priority first
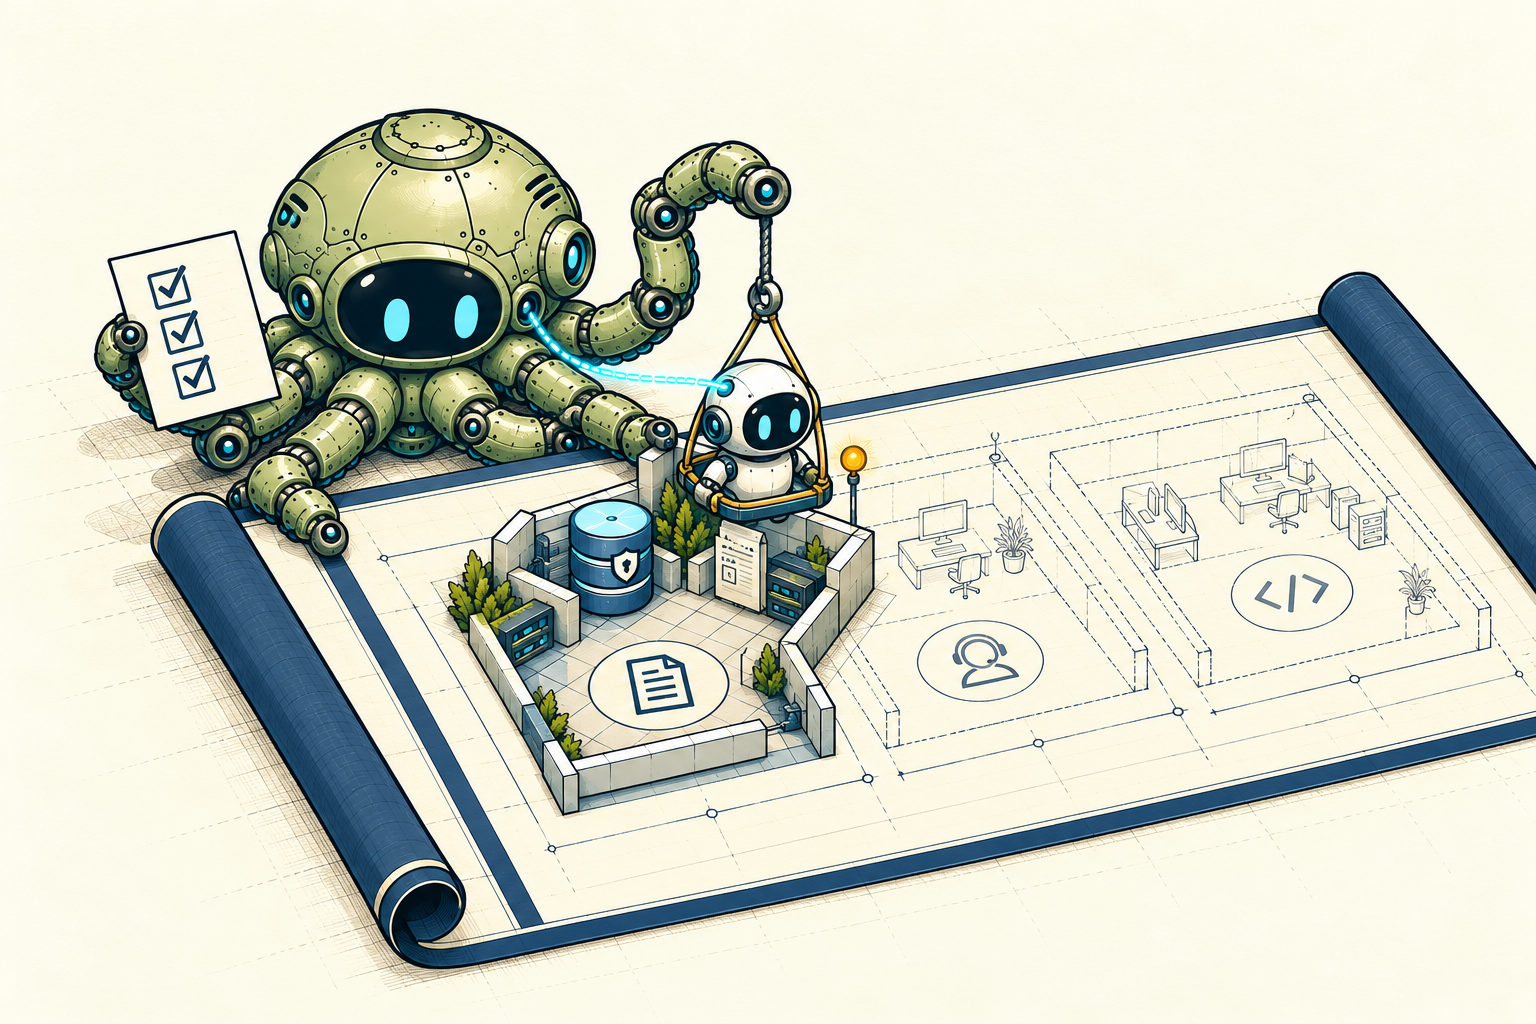
A first deployment should answer a concrete question. Where would unexpected access be important enough for your team to investigate?
- Finance: activity around a synthetic reporting or accounting resource.
- Customer operations: unexpected interaction with an internal service Decoy.
- Development: exploration of a database or application Decoy in an engineering network.
Choose an area your team understands. Give the Decoy a credible role there and configure its reachability intentionally. Keep administration controlled and production credentials out of the Decoy.
A focused deployment is easier to validate and explain. It also gives you a basis for deciding whether another location would add useful visibility.
Start with one business priority, verify the evidence, then decide where to expand.
Test the investigation, not just the installation
With Tero, your team deploys a Sensor in the environment you want to observe, manages its assigned Decoys and reviews the resulting suspicious interactions and recorded evidence in the console.
Once the first Decoy is ready, use an authorized test client to carry out a small, controlled interaction. Then review what your team can actually see.
Check whether the record identifies the right Decoy, preserves the available source context and distinguishes successful actions from denied attempts. Make sure your team can recognize its own test.
The important question is whether someone reviewing the investigation can understand what happened and choose the next step. A running service alone cannot answer that.
Let your visibility grow with your business
Growing companies need detection they can introduce deliberately and evaluate in their own environment. Decoys can complement access controls, endpoint protection, backups and the other measures your team already operates.
Begin with one business priority. Deploy a relevant Decoy, verify the evidence and decide where additional coverage would be useful.
Your next security improvement can start with one place where unexpected access becomes visible—and one investigation your team knows how to follow.